How to Build a Compliance Management System: 8-Step Implementation Guide
Most compliance programs don’t fail because a team missed a rule. They fail because the proof was scattered , a policy in a shared drive, evidence in someone’s inbox, a control nobody clearly owned, and it all surfaced at once during an audit. As regulations multiply and regulators shift from “show us your policy” to “prove it’s working,” that patchwork approach quietly becomes the biggest risk an organization carries. A compliance management system is the fix: not another tool to log into, but the operating model that keeps obligations, controls, ownership, and evidence connected so compliance holds up under scrutiny.
A compliance management system (CMS) is the structured operating model an organization uses to identify the regulations it must follow, assign and run the controls that satisfy them, collect evidence of adherence, and prove that adherence to regulators, auditors, and leadership, continuously, not just at audit time. It combines people, processes, internal controls, and software into one repeatable way of staying compliant as rules change.
The term is not marketing language. In US financial services, regulators including the FDIC, NCUA, OCC, and CFPB formally expect institutions to maintain a compliance management system scaled to the size and risk of their business, and the FFIEC grades its effectiveness on a 1-to-5 scale under the Consumer Compliance Rating System. That regulatory heritage is why “compliance management system” means something more specific than a dashboard: it describes how an organization actually governs compliance.
This guide explains how to build a compliance management system, and how to measure it, and where AI is taking it in 2026.
Key Highlights
What a compliance management system is not
A CMS is a system, not a single tool. It is the connective tissue between four things that otherwise drift apart: the obligations you are subject to, the controls that satisfy them, the people accountable for those controls, and the evidence that proves the controls work.
It is not just a spreadsheet of regulations, and it is not simply the software you log into. A pile of policies with no ownership is not a CMS. A monitoring tool with no governance around it is not a CMS either. The system is what turns scattered compliance activity into a repeatable program that produces proof on demand.
At its core, a mature CMS answers four questions on a continuous basis:
- What are we required to comply with? It maps the laws, regulations, standards, certifications, and internal policies that apply, and keeps that map current as requirements change.
- Who owns each obligation? It assigns clear accountability for every control so nothing is “someone else’s job.”
- Are the controls actually working? It monitors control performance, collects evidence continuously, and flags gaps before they become findings.
- Can we prove it right now? It produces the reports, audit trails, and evidence packages that satisfy regulators, external auditors, and the board at any moment.
When those four questions are answered continuously, audit preparation stops being a fire drill and becomes a matter of running a report.
What Is the Purpose of a Compliance Management System?
A compliance management system creates a structured way for an organization to understand what it must comply with, assign responsibility, put controls in place, monitor whether those controls are working, and maintain evidence that compliance requirements are being met.
Then give five outcomes:
- Reduce compliance risk
- Establish accountability
- Maintain continuous monitoring
- Improve audit and regulatory readiness
- Identify and remediate problems earlier
ISO 37301 and Compliance Management Systems
ISO 37301:2021 is the international standard specifically designed for compliance management systems. It provides requirements and guidance for establishing, developing, implementing, evaluating, maintaining, and continually improving an effective CMS. Organizations can use ISO 37301 as a structured reference for building a compliance program that integrates leadership, compliance obligations, risk assessment, controls, monitoring, reporting, and continuous improvement.
ISO 37301 is useful because a compliance management system should be more than a collection of policies or software tools. The standard treats compliance as a management system that must be embedded into organizational governance, responsibilities, processes, and decision-making. Organizations can use the framework to benchmark an existing CMS, identify gaps, formalize responsibilities, and create a repeatable process for improving compliance performance over time.
Compliance management system vs compliance management software vs GRC
These three terms get used interchangeably and shouldn’t be. The distinction matters the moment you start evaluating tools or budget.
| Term | What it means | Scope |
|---|---|---|
| Compliance management | The overall strategy and discipline of adhering to regulations | Broadest — the approach |
| Compliance management system (CMS) | The operating model that puts that strategy into practice: policies, controls, oversight, evidence, and technology together | The program |
| Compliance management software | The technology layer that operationalizes the system — where you configure frameworks, assign tasks, store evidence, and report | The tooling |
| GRC software | Broader platforms spanning governance and enterprise risk in addition to compliance | Superset of a CMS |
In plain terms: compliance management is the what, a compliance management system is the how, and compliance management software is what you use to run the how. A CMS is one pillar of governance, risk, and compliance (GRC); many platforms serve both a focused CMS and broader GRC needs.
Why a compliance management system matters more in 2026
Compliance has shifted from a periodic exercise to a continuous business function, and three pressures explain why a formal CMS is now table stakes rather than a nice-to-have.
Obligations are multiplying and overlapping. Most organizations no longer answer to a single framework. They juggle federal and state regulation, international requirements, contractual obligations, industry standards, and internal policy simultaneously, and a change in one often ripples across controls mapped to several others.
Regulators want proof, not policies. It is no longer enough to say a control exists. Examiners expect documented processes, assigned ownership, continuous monitoring, supporting evidence, and timely remediation. The US Department of Justice’s 2026 corporate enforcement guidance reinforced that regulators increasingly reward organizations that can demonstrate a functioning program, not just describe one.
Non-compliance is expensive — and public. Fines land in the headlines (regulators have levied billion-dollar penalties for data-protection failures alone), and research has repeatedly found that the cost of non-compliance runs materially higher than the cost of maintaining strong controls — by some estimates more than twice as much once fines, disruption, and remediation are counted. Beyond penalties, buyers now treat a company’s compliance posture as a purchasing criterion.
A CMS is how an organization absorbs all of this without the program collapsing back into spreadsheets and last-minute audit scrambles.
The core components of an effective compliance management system
The canonical model regulators use has three pillars, board and management oversight, a compliance program, and independent testing. A modern CMS keeps those pillars and adds the operational machinery that makes them run day to day.
1. Board and management oversight
Compliance culture is set from the top. The board and senior leadership are ultimately responsible for the program: allocating budget and headcount, approving policy, and demonstrating — through documented deliberation — that they take compliance seriously. Many organizations appoint a chief compliance officer who reports directly to the board and keeps it informed of emerging issues and audit findings.
2. The compliance program
The program is the heart of the CMS. It typically includes:
- Policies and procedures — documented, current, and acknowledged by staff.
- Change management — a process for evaluating how new or amended regulations affect existing controls.
- Training — role-specific education so employees understand both the rules and the “why” behind them.
- Monitoring — ongoing surveillance of whether controls are operating as intended.
- Complaint response — a standardized process for handling and learning from consumer or stakeholder complaints, which regulators scrutinize closely.
- Corrective action — root-cause analysis and remediation when gaps or violations surface.
3. Independent audit and testing
Internal or external audits provide an impartial check on whether the program actually works. They validate control effectiveness, create a historical record, and can be shared with regulators to demonstrate accountability. Independence is what gives an audit its weight.
The operational layer that ties it together
The three pillars only function if the day-to-day mechanics are in place: a control library mapped to frameworks, task assignment with deadlines and escalation, evidence attached directly to controls, audit trails, and real-time dashboards that give leadership a shared view of program health. This operational layer is where compliance management software earns its keep.
Who Needs a Compliance Management System?
A compliance management system is most valuable for organizations that operate in regulated industries, manage multiple compliance requirements, or need to coordinate compliance responsibilities across several departments, locations, or business entities. As the number of regulations, controls, policies, owners, and evidence requirements grows, relying on spreadsheets, shared folders, and manual follow-ups becomes increasingly difficult to manage consistently.
Industries such as financial services, healthcare, energy and utilities, insurance, manufacturing, pharmaceuticals, technology, higher education, and food and beverage often have a particularly strong need for a structured CMS. These organizations may need to manage recurring regulatory obligations, policy requirements, internal controls, assessments, audits, incidents, corrective actions, and supporting evidence throughout the year.
A formal compliance management system is especially useful when an organization:
- Operates under multiple regulations, standards, or contractual requirements
- Has compliance responsibilities distributed across different teams or locations
- Completes recurring compliance reviews, assessments, or control testing
- Needs to provide evidence regularly to regulators, auditors, customers, or leadership
- Manages large numbers of policies, controls, obligations, and corrective actions
- Has experienced repeated audit findings, missed deadlines, or unclear compliance ownership
- Is expanding into new markets, jurisdictions, entities, or regulated business activities
The need for a CMS is therefore driven less by company size than by compliance complexity. Even a smaller organization may need a structured compliance system if its regulatory requirements are significant, while larger organizations typically need stronger governance, automation, monitoring, and reporting to maintain consistent oversight across the business.
Benefits of a Compliance Management System
| Benefit | How a CMS Helps |
|---|---|
| Clear Accountability | Assigns owners to obligations, controls and corrective actions |
| Reduced Compliance Risk | Identifies control gaps and overdue activities earlier |
| Audit Readiness | Maintains evidence and audit trails continuously |
| Consistent Processes | Standardizes compliance activities across teams and locations |
| Better Visibility | Gives compliance leaders dashboards and status reporting |
| Faster Remediation | Tracks findings and corrective actions through closure |
| Reduced Manual Work | Replaces spreadsheets and repetitive follow-ups with structured workflows |
| Scalability | Supports additional regulations, entities and locations as the organization grows |
Compliance management system examples
Examples of a Compliance Management System in Practice
Consider a hospital system operating across several locations.
Its CMS could maintain healthcare privacy and security requirements, assign controls to privacy, IT, HR, and clinical teams, schedule recurring assessments, manage policy reviews, track employee attestations, collect evidence, record incidents, and monitor corrective actions.
An energy company might use the same operating model differently. Regulatory requirements could be mapped to facilities, controls, inspections, responsible engineers, recurring obligations, evidence, findings, and management reporting.
In financial services, a CMS might connect regulatory requirements with business processes, policies, monitoring activities, complaints, training, testing, issues, service-provider oversight, and examination evidence.
The regulations change, but the underlying model remains similar:
Requirement → Control → Owner → Activity → Evidence → Monitoring → Issue → Remediation → Reporting
- A regional bank runs its CMS around the FFIEC framework — board oversight, consumer-complaint handling, and independent testing tied to consumer-protection laws.
- A hospital network centers its CMS on HIPAA — policy attestations, access controls, incident logging, and continuous evidence for audits.
- An electric utility builds its CMS around NERC and FERC reliability standards, where evidence management and audit readiness are operational and year-round rather than a single filing.
- A SaaS company may anchor its CMS in SOC 2 and ISO 27001, with automated evidence collection from its cloud stack.
- A manufacturer structures its CMS around safety, environmental, and quality standards, with field audits and corrective-action tracking.
That traceability is one of the defining characteristics of an effective compliance management system.
The common thread: obligations mapped, controls owned, evidence captured, proof produced. Only the frameworks and cadence change.
How to build a compliance management system: a step-by-step approach
Building a CMS is less about buying software and more about establishing a repeatable operating model. A practical sequence:
- Map your obligations. Inventory every regulation, standard, contractual requirement, and internal policy you answer to. This becomes your obligation register.
- Define and map controls. Translate each obligation into concrete controls, and map single controls to multiple requirements to avoid duplicate work.
- Assign ownership. Give every control a named owner with clear expectations and deadlines. Accountability is the difference between a plan and a program.
- Establish monitoring and evidence collection. Decide how each control is tested and how evidence is captured — ideally continuously, so it accumulates rather than being gathered reactively.
- Set up reporting and oversight. Build dashboards and reporting cadences that give the board and compliance leaders a live view of program status.
- Train and drive adoption. A CMS only works if people use it. Train by role, explain the “why,” and make participation part of daily work.
- Audit, remediate, and improve. Run independent testing, perform root-cause analysis on gaps, remediate promptly, and feed lessons back into the program.
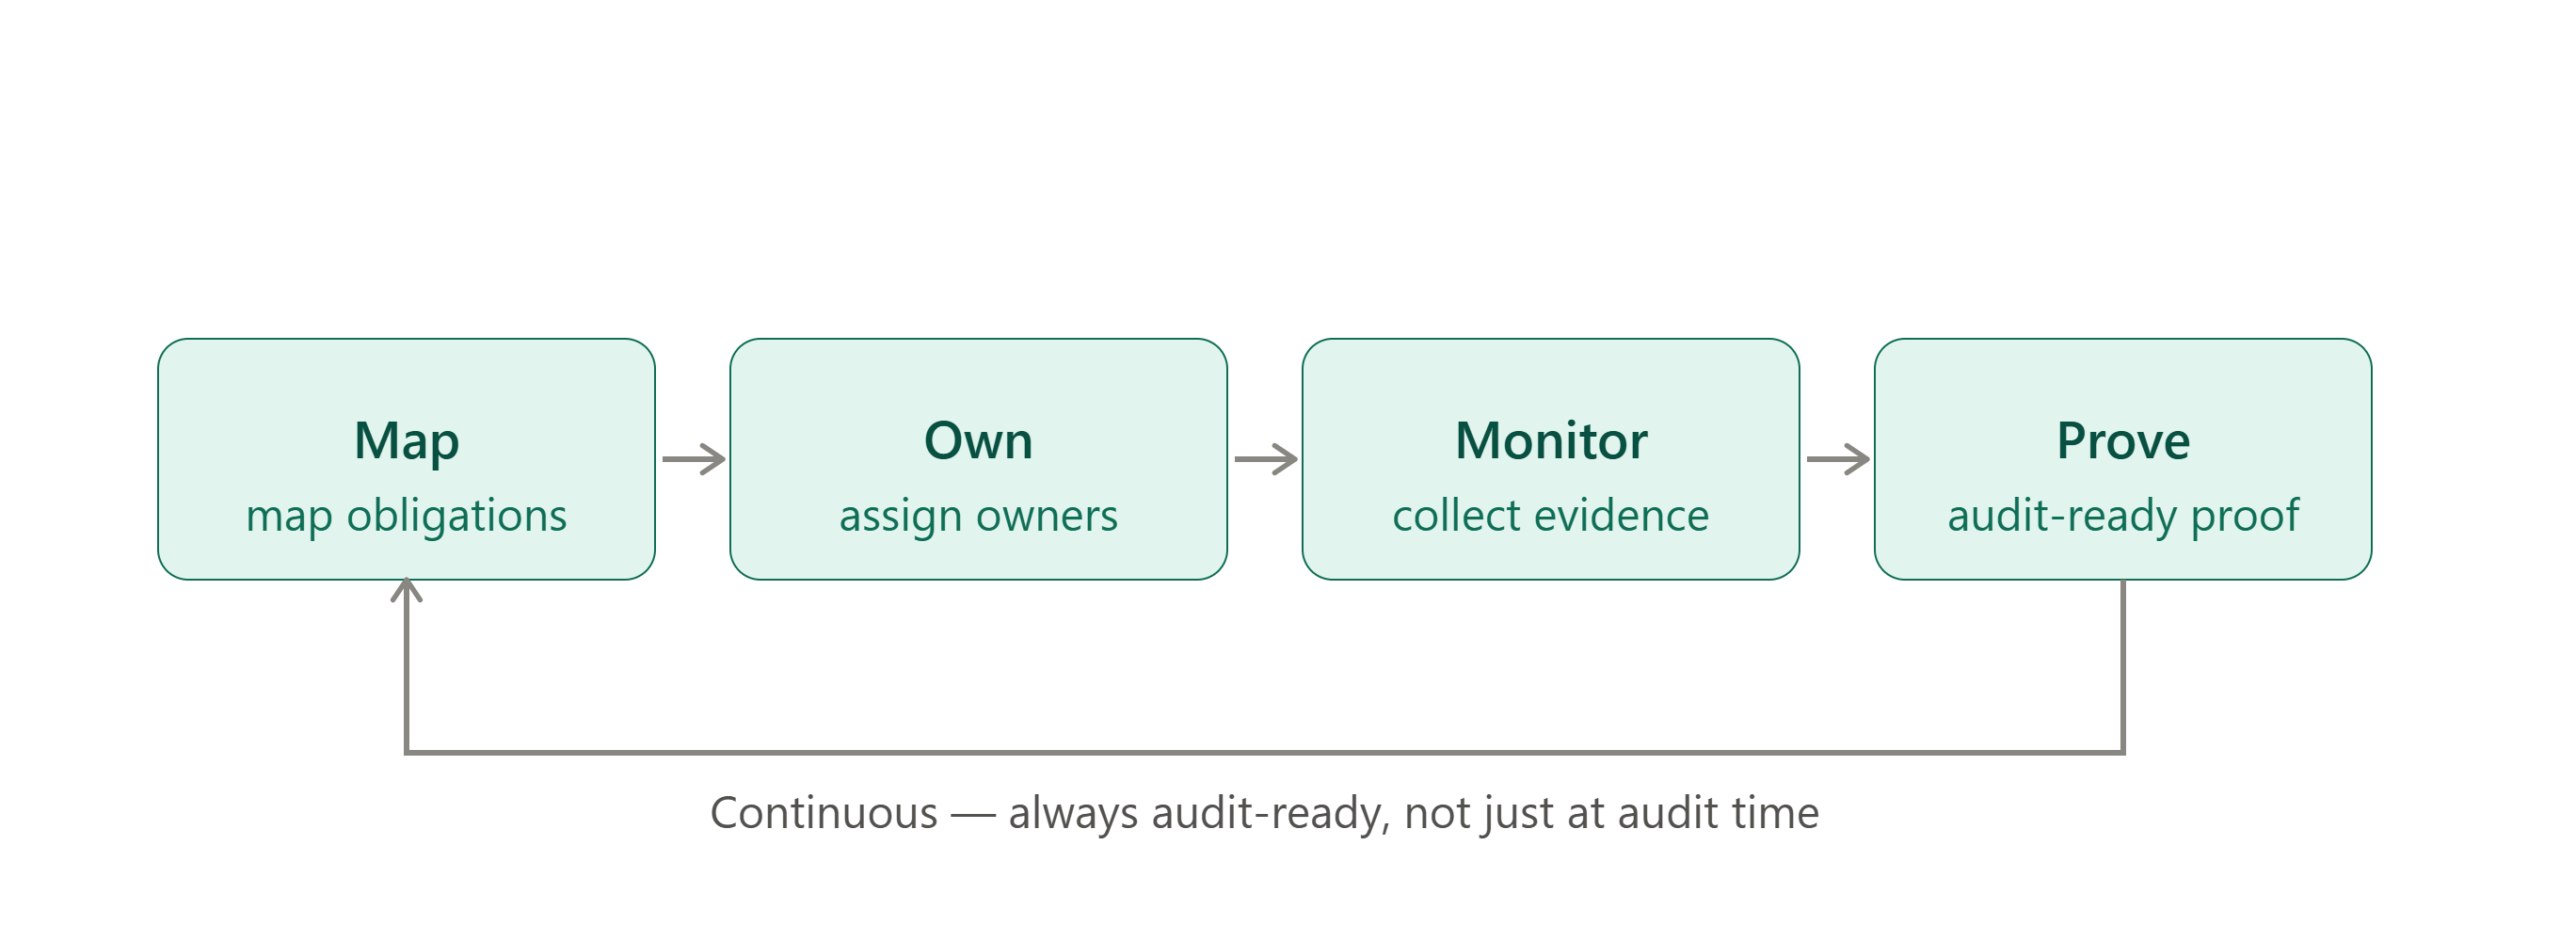
From reactive to continuous: the CMS maturity curve
Most compliance programs sit somewhere on a maturity curve, and knowing where you are tells you what to fix next.
| Stage | What it looks like | Risk profile |
|---|---|---|
| Reactive | Spreadsheets, email evidence, audit-time scrambles | High — gaps found during audits |
| Managed | Centralized policies and a control library, manual monitoring | Moderate — visibility exists but lags |
| Proactive | Assigned ownership, scheduled testing, dashboards | Lower — issues caught before findings |
| Continuous | Automated evidence, continuous control monitoring, AI-assisted mapping | Lowest — always audit-ready |
The goal of a modern CMS is to move an organization up this curve — from finding out about problems during an audit to knowing about them the moment they occur.
How to Measure Whether a CMS Is Effective
A useful CMS should produce measurable information about compliance performance.
Organizations can monitor indicators such as the percentage of obligations completed on time, overdue compliance activities, control effectiveness, failed assessments, unresolved findings, average remediation time, policy review completion, employee attestations, evidence completeness, recurring issues, regulatory changes awaiting implementation, and audit findings by severity.
No single metric proves that an organization is compliant.
The goal is to combine indicators that show execution, effectiveness, risk, and improvement.
For example, a 98% task-completion rate may look strong, but it tells only part of the story if the remaining 2% contains high-risk regulatory obligations. Likewise, having zero open findings could indicate a strong program, or an ineffective monitoring process that is failing to identify problems.
Metrics need context.
Compliance Management System Maturity
Not every CMS begins at the same level of maturity.
A reactive CMS depends heavily on spreadsheets and people remembering what needs to happen. Compliance teams spend significant time chasing evidence and preparing for audits.
A managed CMS introduces defined owners, recurring schedules, documented controls, centralized evidence, and regular reporting.
A proactive CMS uses risk-based monitoring, automated workflows, control testing, escalation, dashboards, and structured remediation to identify problems earlier.
A continuous CMS integrates compliance into daily business operations. Requirements, controls, risks, evidence, issues, and regulatory changes are connected, giving management ongoing visibility rather than periodic snapshots.
Organizations do not need to automate everything to reach maturity. The objective is to make compliance repeatable, measurable, accountable, and responsive to change.
The Role of Compliance Management Software
Technology becomes increasingly valuable as the compliance system scales.
Compliance management software can centralize regulatory obligations, automate recurring tasks, send reminders and escalations, manage controls, collect evidence, support assessments, track issues, maintain audit trails, manage policies, and provide dashboards.
Software can also reduce fragmentation.
Instead of maintaining obligations in one spreadsheet, evidence in shared drives, policies in another system, risks somewhere else, and corrective actions through email, organizations can connect these activities through a common compliance structure.
However, software should support the CMS rather than define it.
Before selecting a platform, organizations should understand what they need to manage, who owns each process, how controls operate, what evidence is required, and what management needs to see.
Start your 21-day free trial and experience how VComply helps you with compliance maturity.
Benefits of a Compliance Management System
| Benefit | How a CMS Helps |
|---|---|
| Clear Accountability | Assigns owners to obligations, controls and corrective actions |
| Reduced Compliance Risk | Identifies control gaps and overdue activities earlier |
| Audit Readiness | Maintains evidence and audit trails continuously |
| Consistent Processes | Standardizes compliance activities across teams and locations |
| Better Visibility | Gives compliance leaders dashboards and status reporting |
| Faster Remediation | Tracks findings and corrective actions through closure |
| Reduced Manual Work | Replaces spreadsheets and repetitive follow-ups with structured workflows |
| Scalability | Supports additional regulations, entities and locations as the organization grows |
How AI Fits Into a Modern CMS
AI can make parts of compliance management faster, but it should not replace accountable human judgment.
Useful applications include summarizing regulatory updates, helping teams search policies, identifying potentially missing evidence, suggesting relationships between requirements and controls, summarizing assessment results, and highlighting items that may require attention.
The DOJ’s current compliance-program guidance also considers how companies govern their own use of emerging technologies, including whether risks are assessed and controls are implemented appropriately.
That creates an important distinction.
AI can be a tool inside the compliance management system, but the organization’s use of AI may also become something the compliance management system itself must govern.
For this reason, organizations should establish appropriate review, approval, access, validation, and accountability processes around AI-assisted compliance work.
Common Compliance Management System Mistakes
One common mistake is treating a CMS as a document repository. Policies and evidence are important, but a folder full of documents does not establish ownership, monitoring, control effectiveness, or remediation.
Another is treating compliance as the compliance team’s responsibility alone. Effective systems distribute ownership to the people who operate the relevant business processes while giving compliance teams appropriate oversight.
Organizations also struggle when they track activities without connecting them to requirements. A completed task has limited value if nobody can explain which obligation or control it supports.
Finally, many programs focus heavily on identifying issues but less on verifying remediation. Closing a finding should require confidence that the underlying problem has actually been addressed.
Compliance management system readiness checklist
Knowing what a compliance management system should do is one thing; knowing whether yours actually does it is another. Use the checklist below as a quick self-assessment, each item reflects a capability that separates a program that merely exists from one that holds up under regulatory scrutiny. If you can confidently check every box, your CMS is operating at a continuous, audit-ready maturity level. If a few are missing, those gaps are the most useful place to focus next.
- Every applicable regulation, standard, and internal policy is inventoried and current.
- Each obligation maps to at least one owned control.
- Every control has a named owner, a deadline, and an escalation path.
- Evidence attaches directly to controls, with a complete audit trail.
- Monitoring is continuous, not audit-triggered.
- Leadership has real-time visibility into program health.
- Independent audit and corrective-action processes are in place.
- The program adapts when regulations change.
Your compliance management system is only as strong as your ability to prove it’s working, on any day, not just audit day. VComply brings compliance, risk, policy, and audit into one configurable platform, so obligations stay mapped, controls stay owned, and evidence accumulates continuously instead of in a last-minute scramble. It’s built for the regulated operational industries where compliance runs year-round, healthcare, energy and utilities, financial services, education, and manufacturing. See how VComply turns a fragmented program into a connected, always-audit-ready system. Book a demo or start your free trial today.
Frequently asked questions
What is a compliance management system?
A compliance management system (CMS) is the framework an organization uses to identify its regulatory obligations, build and assign controls to meet them, collect evidence of adherence, and prove compliance to regulators and auditors. It combines people, processes, internal controls, and software into one continuous operating model.
What is the difference between a compliance management system and compliance management software?
The system is the broader operating model — policies, processes, oversight, and technology together. The software is the technology layer that runs the system by configuring frameworks, assigning tasks, storing evidence, and generating reports.
What are the main components of a compliance management system?
Board and management oversight, a compliance program (policies, change management, training, monitoring, complaint response, and corrective action), and independent audit and testing — supported by an operational layer of control libraries, task management, evidence, and reporting.
Is a compliance management system the same as GRC software?
No. A CMS is one part of governance, risk, and compliance (GRC). GRC software typically spans governance and enterprise risk in addition to compliance. Many platforms serve both.
Who is required to have a compliance management system?
Any organization with regulatory, contractual, or internal-policy obligations benefits from one, and regulated institutions — banks, credit unions, healthcare providers, utilities — are formally expected by their regulators to maintain one.
How do you build a compliance management system?
Map your obligations, define and map controls, assign ownership, establish monitoring and evidence collection, set up reporting and oversight, train staff, and run ongoing audit and remediation.
How much does a compliance management system cost?
Most mid-market and enterprise platforms use quote-based pricing that varies with modules, users, and frameworks, so request a tailored quote rather than relying on list figures.