Risk Mitigation Strategies: How to Reduce Business Risk
Risk management is the systematic process of identifying, evaluating, and addressing potential risks that could impact an organization’s operations, objectives, or goals. Organizations encounter various types of risks, and these can broadly be categorized into financial risks, operational risks, reputational risks, compliance risks, safety risks, etc.
Business risks become easier to manage when organizations connect them with clear decisions, practical safeguards, and accountable owners. Supplier delays, unauthorized payments, system outages, and missed compliance responsibilities require different responses, but each needs a structured approach.
Risk mitigation is the process of reducing the likelihood or impact of events that could affect business objectives. It can involve strengthening controls, improving processes, building alternative capacity, or preparing recovery arrangements.
This guide explains common approaches to managing risk, how to choose appropriate mitigation measures, and how to evaluate whether those measures are working.
Key takeaways (TL;DR)
-
Learn how a structured risk management plan identifies, assesses, and prioritizes potential organizational threats.
-
Discover proven strategies like risk transfer, buffering, and contingency planning to minimize disruptions.
-
Explore the importance of continuous monitoring, communication, and data-driven decision-making in risk management.
-
See how risk digitization and automation tools streamline mitigation efforts and enhance business resilience.
-
Get insights into how VComply empowers organizations to simplify risk evaluation and drive compliance success.
How a Risk Management Plan Supports Mitigation.
A risk management plan establishes how an organization identifies, assesses, responds to, and monitors risks. Within that plan, mitigation actions explain what will change, who will implement the change, and how results will be evaluated. Each significant action should have an owner, deadline, supporting evidence, and a defined review process.
Now that we’ve discussed the components of a risk management plan, let’s delve into the essential approaches for mitigating risks effectively.
Approaches to Managing and Mitigating Risk.
Organizations can avoid, reduce, transfer, share, or accept risk, depending on the circumstances. Mitigation focuses on reducing exposure, while measures such as contingency planning and resource buffers help limit disruption. Testing and digital tools support these approaches by helping teams evaluate safeguards and coordinate follow-up.
| Approach | Refined explanation |
|---|---|
| Risk acceptance | An authorized decision to retain exposure when further treatment is not justified or feasible. Document the rationale, accountable owner, and conditions requiring review. |
| Risk avoidance | Stop, decline, or change an activity to remove a particular exposure. Consider the operational and commercial consequences of that decision. |
| Risk transfer | Use insurance or contractual arrangements to allocate specified consequences to another party. Review exclusions and limits because some exposure remains. |
| Risk sharing | Distribute defined responsibilities or consequences among partners. Establish clear agreements, oversight, and arrangements for handling failures. |
| Risk buffering | Maintain appropriate reserves of time, funds, inventory, or capacity to absorb disruption. Review whether those reserves remain sufficient and economical. |
| Contingency planning | Define what happens if an event occurs, including activation triggers, decision authority, communication, and recovery priorities. Test the arrangements. |
| Control testing | Evaluate whether safeguards are suitably designed and operate as intended. Investigate exceptions and verify corrective actions. |
| Risk reduction | Introduce controls or process improvements that lower likelihood, impact, or both. Examples include independent approvals, access restrictions, and preventive maintenance. |
| Digital support | Use software to connect risk records, controls, owners, actions, and reporting. Technology supports execution; its presence alone does not establish risk reduction. |
How to Choose the Right Risk Mitigation Strategy
Select mitigation measures based on the risk’s causes, potential consequences, and the organization’s tolerance for exposure. Consider existing controls, implementation costs, available resources, and how quickly protection is needed. A recurring payment error may require stronger validation and independent review, while dependence on one supplier may call for alternative sourcing and contingency arrangements. Several measures may work together, but each should address a specific weakness. Risk acceptance should be documented as a response decision; acceptance alone does not reduce exposure.
Risk Mitigation in Practice: Managing Supplier Disruption
Lets explain risk mitigation in practice with an example. A business depends on one supplier for a component essential to production. Increasing delivery delays create a risk of missed customer commitments.
The procurement team qualifies an alternative supplier, reviews inventory requirements, and introduces regular monitoring of delivery performance. Each action receives an owner and deadline, while agreed thresholds determine when delays require escalation.
Management then checks whether the alternative supplier can meet quality and capacity requirements. It reassesses the remaining exposure using delivery results and readiness evidence. This connects the mitigation plan with demonstrable protection rather than task completion alone.
Turn Mitigation Decisions Into an Action Plan
A mitigation strategy becomes actionable when it specifies what must change, who will deliver it, and when completion is expected. Record each action alongside its associated risk, accountable owner, deadline, required resources, and completion criteria. For example, “improve supplier resilience” could become an action to qualify an alternative supplier, test its capacity, and document approved purchasing arrangements. Identify dependencies and escalation routes so delays reach the appropriate decision-maker. This helps prevent agreed measures from remaining unresolved in meeting notes or disconnected task lists.
Evaluate Residual Risk Using Evidence
Residual risk is the exposure remaining after controls and other treatment measures are considered. Reassess it using evidence that safeguards are appropriately designed and operating as intended. An approved recovery plan, for example, provides limited reassurance without a successful restoration test. Review testing exceptions, incidents, operational indicators, and unresolved weaknesses before changing a risk rating. Where exposure remains above approved tolerance, management should strengthen treatment, reconsider the activity, or seek an authorized acceptance decision. Completing mitigation tasks should not automatically produce a lower risk score.
Review Mitigation Plans When Conditions Change
Mitigation plans should evolve with the activities they protect. New systems, acquisitions, supplier changes, staffing constraints, regulatory developments, and incidents can alter exposure or weaken existing safeguards. Establish scheduled reviews alongside event-based triggers, and involve the people responsible for the affected processes. Check whether ownership, control coverage, response arrangements, and escalation thresholds remain appropriate. Use lessons from incidents and near misses to address underlying causes, then verify that corrective actions work. This keeps mitigation connected to current operations rather than assumptions recorded during an earlier assessment.
Taking Control of Your Risk with VComply
VComply is a comprehensive compliance and risk management software that helps organizations streamline and automate their risk assessment and management. With features like centralized data management, risk scoring, a risk register, customizable workflows, and real-time reporting, VComply empowers businesses to identify and mitigate risks proactively, ensuring regulatory compliance and fostering a culture of effective risk management. VComply empowers organizations to proactively manage risks, make informed decisions, and drive risk awareness and mitigation. By implementing the VComply platform, organizations can confidently navigate the complexities of risk management.
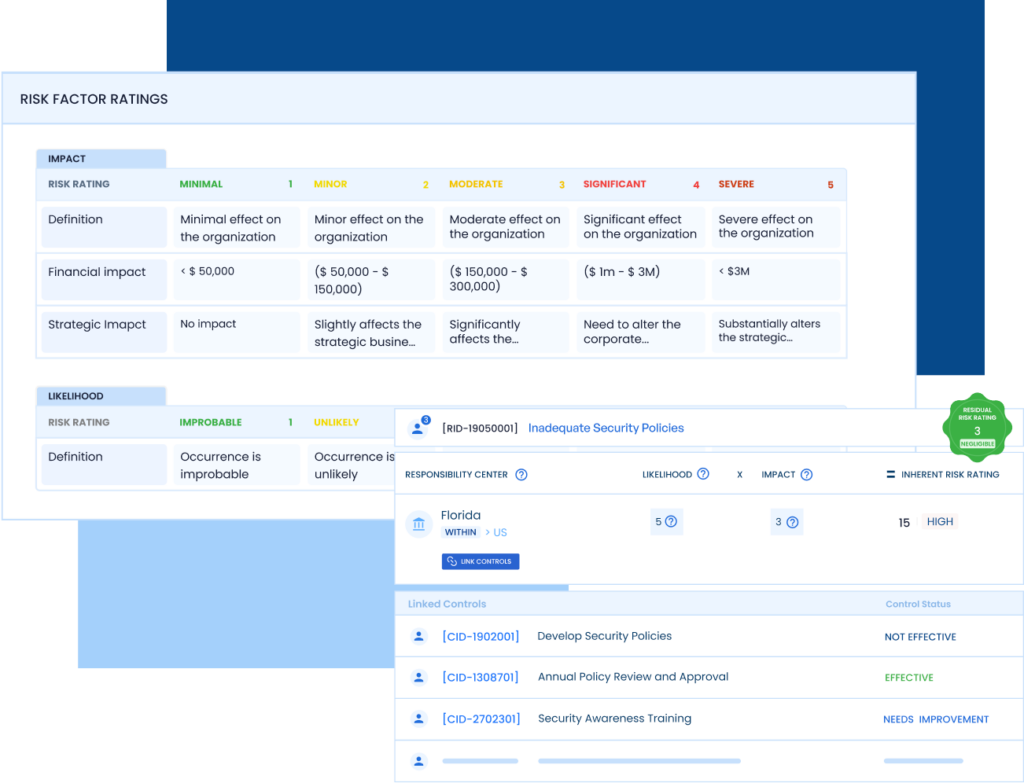
Is your organization looking to streamline its risk management procedures? Explore VComply’s risk management tool as a dependable solution for simplifying the processes of risk evaluation, mitigation, and monitoring, enhancing the efficiency and effectiveness of your organization’s risk management efforts. With features such as inherent and residual risk assessment, dynamic dashboards, adaptable reporting, collaborative risk workrooms, and the assignment of control measures, VComply enables organizations to take a proactive approach to risk management, make well-informed decisions, and foster a culture of risk awareness and mitigation.
To discover more about how VComply can benefit your business, request a demo today.
Frequently Asked Questions
What are risk mitigation strategies?
Risk mitigation strategies are measures used to reduce the likelihood or impact of adverse events. Examples include approval controls, preventive maintenance, alternative suppliers, access restrictions, and tested recovery procedures.
How do you choose a risk mitigation strategy?
Consider the risk’s causes, likelihood, potential consequences, existing controls, and available resources. Select measures that address the exposure and define how their effectiveness will be evaluated.
What is the difference between risk mitigation and risk avoidance?
Risk mitigation reduces exposure while an activity continues. Risk avoidance removes a particular exposure by stopping, declining, or substantially changing the activity that creates it.
What should a risk mitigation plan include?
A plan should document the risk, accountable owner, mitigation actions, deadlines, resources, completion evidence, and monitoring arrangements. It should also explain when unresolved issues require escalation.
How do you measure whether risk mitigation is effective?
Review control-test results, operational indicators, recurring incidents, and unresolved exceptions. Use this evidence to reassess residual risk, rather than relying only on completed tasks.
When should risk mitigation strategies be reviewed?
Review them on a schedule appropriate to the exposure and after significant changes, incidents, or control failures. Update measures when their assumptions, scope, or effectiveness no longer reflect current conditions.