People, Process, and Technology: The Three Pillars of Effective Compliance Management
Organizational exposure to compliance risk is increasing consistently while compliance costs are skyrocketing. A reactive approach to compliance creates complexity and forces organizations to be less agile. Previously, organizations viewed compliance as discrete obligations and created multiple siloed initiatives to meet the objectives. These initiatives typically rely on manual compliance management processes burdened with costly assessments managed using error-prone spreadsheets, documents, and email. This reactive methodology makes adapting to new regulatory requirements and changing business environments difficult.
Organizations today face growing regulatory expectations, increased operational complexity, and greater pressure to demonstrate accountability. Compliance is no longer limited to preparing for audits or maintaining policies in shared drives. It has become an operational discipline that affects risk management, governance, employee accountability, and business continuity.
Many organizations struggle with compliance not because they lack effort, but because their compliance programs are fragmented. Responsibilities are unclear, processes vary across teams, and technology systems fail to provide visibility.
This is where the three pillars of effective compliance management become important: People, Process, and Technology.
These pillars work together to create a compliance program that is organized, measurable, and sustainable.
Key Highlights
- Effective compliance programs rely on people, process, and technology working together.
- People drive accountability through ownership, training, and leadership support.
- Processes create repeatable workflows and audit-ready execution.
- Technology improves visibility, tracking, reporting, and evidence management.
- Organizations that balance all three pillars reduce compliance gaps and improve operational control.
- Compliance software helps connect policies, controls, responsibilities, and reporting in one centralized environment.
What Are the Three Pillars of Compliance Management?
The three pillars of compliance management refer to the foundational elements required to build and maintain an effective compliance program:
- People – the individuals responsible for carrying out compliance activities and maintaining accountability.
- Process – the workflows, procedures, and controls that standardize how compliance work is performed.
- Technology – the systems and tools used to manage policies, evidence, reporting, monitoring, and oversight.
A compliance program becomes difficult to manage when any of these pillars are weak.
For example:
- Strong policies without employee accountability often lead to missed obligations.
- Dedicated teams without standardized processes create inconsistency.
- Technology without defined ownership and workflows produces poor adoption and limited value.
Organizations that succeed in compliance understand that these three pillars must work together rather than operate independently.
The Importance of People, Processes, and Technology in Compliance Management
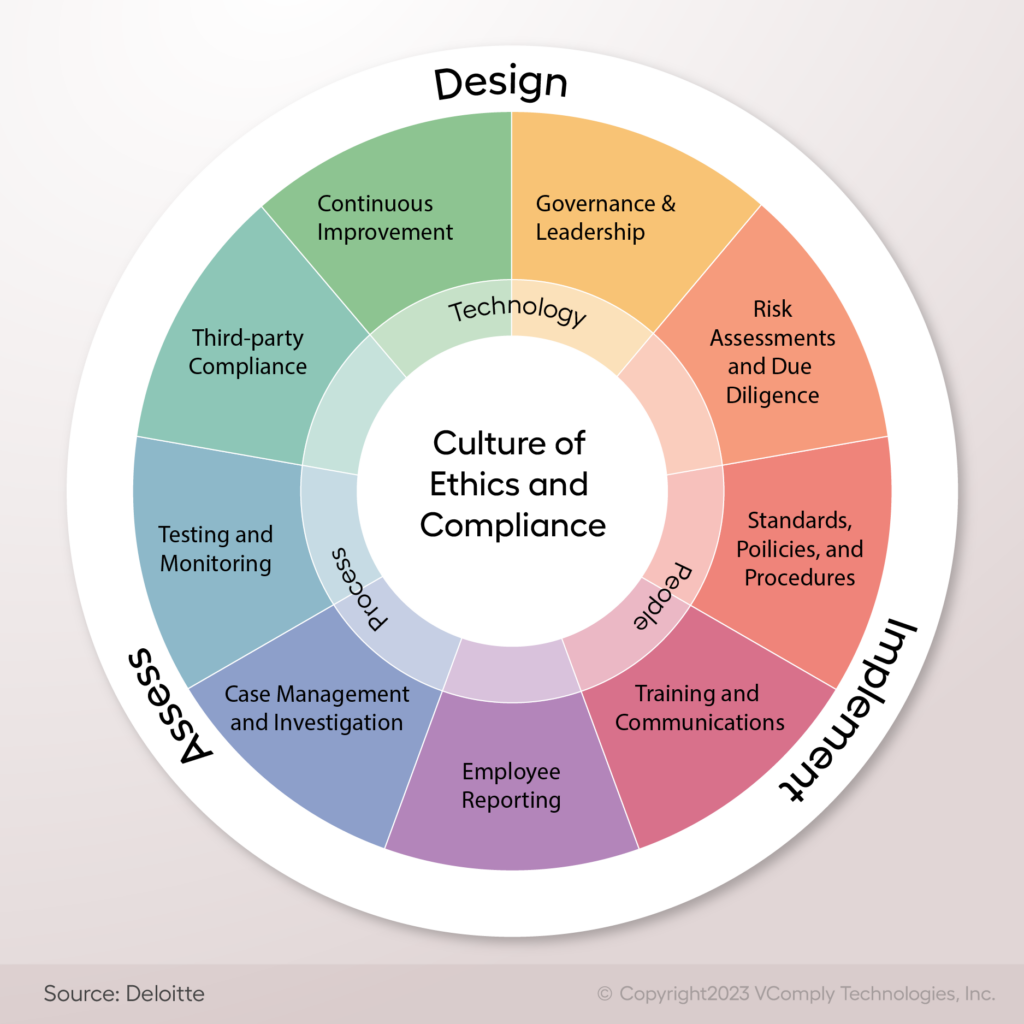
With the constantly rising risk factors and challenges as well as regulatory changes a business faces, the compliance management process is no more sidelined as a mere obligation, rather it has become a critical solution to navigate the challenging times as a consolidated, systematic framework helps organizations avoid high penalties, security breaches, and incorrigible reputational damage.
To safeguard an organization, the compliance management framework must be covered in all three aspects – people, process, and technology.
Why People, Process, and Technology Matter More in 2026
Regulatory expectations continue to evolve across industries including healthcare, energy, financial services, manufacturing, and critical infrastructure.
Compliance teams now face challenges such as:
- Growing regulatory complexity
- Distributed and remote workforces
- Increased documentation requirements
- Faster audit cycles
- Cybersecurity and privacy concerns
- Third-party and vendor oversight
- Greater board-level scrutiny
Manual approaches create additional pressure
Many organizations still depend on:
- Spreadsheets
- Email approvals
- Shared folders
- Manual reminders
- Decentralized evidence collection
- Siloed reporting
These methods often create delays and reduce visibility.
Modern compliance management requires a more operational approach where ownership, workflows, and oversight are connected.
The people-process-technology model provides that structure.
The Three Pillars at a Glance
| Pillar | Primary Goal | Core Focus |
|---|---|---|
| People | Accountability | Ownership, training, leadership |
| Process | Consistency | Workflows, controls, repeatability |
| Technology | Visibility | Automation, monitoring, reporting |

Organizations that invest equally across these pillars often experience:
- Better audit preparedness
- Faster issue resolution
- Improved policy adoption
- Stronger regulatory reporting
- Reduced operational risk
- Higher employee accountability
The next step is understanding each pillar in detail and how they contribute to effective compliance management.
Where do People Fit in the Compliance Management Strategy?
A compliance function starts with people. For organizations, people can be the greatest asset or the biggest burden in managing compliance. They play a pivotal role in any compliance management strategy, serving as the linchpin that ensures its effectiveness. They are responsible for understanding, implementing, and upholding regulatory requirements within an organization, making their engagement, training, and commitment essential components of a robust compliance framework.
Pillar 1: People, Building Accountability and Compliance Ownership
Compliance programs do not fail because policies are missing. They often fail because ownership is unclear.
The first pillar of effective compliance management is People.
People are responsible for understanding requirements, following policies, completing assigned actions, documenting evidence, and responding to regulatory obligations. Without clear accountability, even well-designed compliance programs become inconsistent.
This pillar includes:
- Leadership commitment
- Defined responsibilities
- Employee awareness
- Training and communication
- Department-level accountability
- Continuous engagement
Compliance should not operate as a standalone department.
Effective programs distribute responsibility across the organization while maintaining central oversight.
Why People Matter in Compliance Management
Regulations may define requirements, but people carry them out.
Every compliance activity ultimately depends on someone taking action.
Examples include:
- Reviewing and approving policies
- Completing training requirements
- Performing inspections
- Maintaining records
- Conducting control testing
- Managing vendor reviews
- Investigating incidents
- Responding to audits
When ownership is unclear, organizations often experience:
- Missed deadlines
- Delayed approvals
- Incomplete evidence
- Duplicate work
- Poor audit performance
- Reduced accountability
This creates operational and regulatory risk.
A strong people framework establishes clarity around who owns what and when actions are expected.
Leadership Sets the Compliance Culture
Leadership involvement is one of the strongest indicators of compliance program effectiveness.
Employees often mirror leadership priorities.
If leadership treats compliance as an administrative requirement, teams may view it as a periodic task rather than an operational responsibility.
When leadership actively supports compliance, organizations typically see:
- Better participation
- Faster issue escalation
- Stronger policy adoption
- Higher training completion rates
- Greater accountability
Leadership support includes:
- Setting compliance expectations
- Communicating importance
- Allocating resources
- Reviewing performance metrics
- Supporting remediation efforts
This creates a culture where compliance becomes part of operational decision-making.
Defining Ownership and Responsibility
One of the most common causes of compliance gaps is unclear ownership.
Organizations often rely on broad assumptions such as:
- “Legal owns compliance”
- “Quality manages this”
- “Someone already reviewed it”
These assumptions create risk.
Effective compliance programs assign ownership at multiple levels.
Typical ownership structures include:
| Responsibility | Example Owner |
|---|---|
| Policy oversight | Compliance officer |
| Operational controls | Department manager |
| Training completion | HR and supervisors |
| Evidence collection | Task owner |
| Audit coordination | Compliance team |
| Issue remediation | Assigned business leader |
This approach creates accountability and prevents ownership gaps.
Many organizations use a RACI model to clarify responsibilities:
- Responsible – completes the task
- Accountable – owns the outcome
- Consulted – provides input
- Informed – receives updates
Clear responsibility mapping reduces confusion and improves execution.
Employee Training and Awareness
Training is another essential component of the people pillar.
Policies and procedures only work when employees understand:
- What is required
- Why it matters
- How responsibilities apply to their role
- What actions must be taken
Generic annual training is often insufficient.
Organizations increasingly move toward role-based compliance education.
Examples include:
- Privacy training for healthcare teams
- Cybersecurity awareness for IT staff
- Safety compliance for field operations
- Financial control training for accounting teams
- Vendor compliance guidance for procurement teams
Role-specific training improves relevance and participation.
Training should also be continuous.
Regulations change, policies evolve, and operational risks shift over time.
Ongoing awareness programs help employees stay informed and prepared.
Communication Strengthens Compliance Participation
Communication is often overlooked within compliance programs.
Employees may ignore requirements when communication is inconsistent or unclear.
Common communication challenges include:
- Policy updates buried in email
- Missing reminders
- Limited visibility into due dates
- No confirmation of acknowledgment
- Delayed escalation
Clear communication improves participation and reduces missed actions.
Effective programs use:
- Scheduled reminders
- Approval notifications
- Policy acknowledgment tracking
- Escalation workflows
- Dashboard visibility
These mechanisms support accountability and reinforce expectations.
Compliance Is a Shared Responsibility
A mature compliance program moves beyond department ownership and creates organization-wide participation.
Compliance should involve:
- Leadership
- Operations
- Legal
- HR
- IT
- Risk teams
- Quality teams
- Business managers
This shared-responsibility model improves visibility and reduces dependency on a small central team.
Organizations that rely solely on compliance departments often face scaling challenges.
Distributed accountability supports long-term sustainability.
Common People-Related Compliance Challenges
Organizations frequently encounter several people-related barriers:
| Challenge | Operational Impact |
| Unclear ownership | Missed obligations |
| Weak leadership engagement | Low participation |
| Inadequate training | Errors and policy violations |
| Poor communication | Delays and incomplete actions |
| Department silos | Inconsistent execution |
These issues are common in spreadsheet-driven environments where responsibilities are not centrally tracked.
Addressing these gaps requires more than training alone.
Organizations also need defined workflows and repeatable execution methods.
This leads to the second pillar of effective compliance management: Process.
Where do Processes Fit in the Compliance Management Strategy?
How you approach compliance management depends on the standards you need to meet, stakeholder buy-in, and available resources. Understanding and mapping these elements serve as the basis for the compliance plan and define roles, responsibilities, and processes accordingly.
Processes are integral to a compliance management strategy as they provide the structured framework through which an organization can achieve and maintain adherence to regulatory requirements and industry standards. These processes encompass a wide range of activities, including risk assessment, policy development, monitoring and auditing, reporting, and corrective actions. Each step in these processes is meticulously designed to ensure that an organization identifies, addresses, and mitigates compliance risks effectively. Moreover, processes help in creating a culture of accountability and transparency within the organization, promoting a systematic approach to compliance management.
Pillar 2: Process, Creating Structure and Repeatable Compliance Execution
People provide accountability, but accountability alone does not guarantee consistency.
The second pillar of effective compliance management is Process.
Processes define how compliance work is performed, reviewed, documented, and monitored across the organization.
Without defined processes, compliance activities often become reactive and inconsistent.
Teams may rely on:
-
Individual judgment
-
Email follow-ups
-
Manual approvals
-
Personal spreadsheets
-
Informal documentation practices
These methods create variation and reduce reliability.
Strong compliance processes establish repeatable workflows that support consistency, transparency, and audit readiness.
What Is a Compliance Process?
A compliance process is a documented and repeatable method used to manage regulatory and policy-related activities.
Processes help organizations answer critical operational questions:
-
What action must occur?
-
Who is responsible?
-
When is it due?
-
What evidence is required?
-
How is completion verified?
-
What happens if deadlines are missed?
When these questions are clearly defined, compliance becomes easier to manage and monitor.
Common compliance processes include:
-
Policy creation and review
-
Regulatory obligation tracking
-
Risk and control assessments
-
Training workflows
-
Vendor compliance reviews
-
Incident reporting and investigations
-
Audit preparation and remediation
-
Evidence collection and retention
Each process creates operational structure.
Why Process Matters in Compliance Management
Many organizations struggle with compliance because execution varies between teams.
For example:
One department may follow documented approval procedures while another relies on email confirmation.
One location may maintain detailed records while another stores evidence inconsistently.
These inconsistencies create risk.
Strong processes help organizations:
-
Standardize execution
-
Reduce manual effort
-
Improve accountability
-
Maintain evidence consistency
-
Support regulatory reporting
-
Reduce dependency on tribal knowledge
A repeatable process reduces ambiguity and makes compliance easier to sustain.
From Reactive Compliance to Operational Compliance
Organizations often begin with reactive compliance.
This approach typically involves:
-
Scrambling before audits
-
Chasing evidence manually
-
Sending repeated reminder emails
-
Searching for documents
-
Responding to issues after they occur
Reactive compliance creates stress and operational inefficiency.
Operational compliance uses defined processes to maintain continuous visibility.
Instead of preparing for compliance periodically, organizations manage compliance continuously.
This shift allows teams to:
-
Monitor obligations proactively
-
Identify gaps earlier
-
Escalate delays faster
-
Maintain current records
-
Support ongoing oversight
Continuous execution is increasingly important in regulated industries.
Core Components of Effective Compliance Processes
Well-designed compliance workflows share several common characteristics.
1. Standardized Procedures
Standardization ensures work is completed consistently.
Documented procedures help teams:
-
Follow defined steps
-
Reduce interpretation differences
-
Improve reliability
-
Maintain consistent records
Examples include:
-
Policy approval procedures
-
Incident escalation workflows
-
Control testing procedures
-
Evidence retention standards
Standardization reduces variation and supports governance.
2. Defined Approval Workflows
Approvals are essential for many compliance activities.
Examples include:
-
Policy approvals
-
Risk acceptance decisions
-
Vendor onboarding
-
Corrective action closure
-
Regulatory submissions
Undefined approval paths often create delays and confusion.
Effective processes establish:
-
Required reviewers
-
Approval sequencing
-
Deadlines
-
Escalation rules
-
Documentation requirements
This ensures decisions are traceable and defensible.
3. Evidence Collection and Documentation
Evidence is central to compliance management.
Organizations must often demonstrate:
-
Policies were acknowledged
-
Tasks were completed
-
Controls operated effectively
-
Training occurred
-
Issues were addressed
Manual evidence collection creates challenges.
Teams may struggle with:
-
Missing files
-
Version confusion
-
Duplicate records
-
Delayed submissions
-
Incomplete documentation
Strong processes define:
-
Required evidence
-
Submission standards
-
Storage methods
-
Retention rules
-
Review procedures
This creates stronger audit readiness.
4. Escalation and Exception Management
Compliance processes should account for delays and non-compliance.
Not every task is completed on time.
Not every issue is resolved immediately.
Organizations need escalation procedures that define:
-
Overdue thresholds
-
Notification rules
-
Management escalation
-
Corrective actions
-
Remediation tracking
Escalation creates visibility before problems become larger operational issues.
5. Periodic Review and Improvement
Compliance processes should not remain static.
Regulations change.
Operations evolve.
Risk priorities shift.
Organizations should periodically review:
-
Workflow effectiveness
-
Completion rates
-
Bottlenecks
-
Policy relevance
-
Control effectiveness
-
Audit findings
Continuous review improves process maturity and operational performance.
Common Process Failures in Compliance Programs
Weak processes often create recurring compliance challenges.
| Process Gap | Operational Consequence |
|---|---|
| Undocumented workflows | Inconsistent execution |
| Manual reminders | Missed deadlines |
| No escalation path | Delayed remediation |
| Decentralized evidence | Audit difficulties |
| Poor version control | Outdated information |
| Inconsistent approvals | Governance gaps |
These problems are particularly common in organizations dependent on spreadsheets and disconnected systems.
As regulatory expectations increase, process maturity becomes increasingly important.
Compliance Process Maturity
Organizations typically progress through several stages of process maturity.
| Stage | Characteristics |
|---|---|
| Ad hoc | Informal and reactive |
| Defined | Documented procedures |
| Managed | Tracked and monitored |
| Integrated | Cross-functional workflows |
| Optimized | Continuous improvement and visibility |
Organizations with mature processes often experience:
-
Better audit performance
-
Faster response times
-
Improved accountability
-
Reduced operational friction
-
Greater executive visibility
However, even strong processes have limitations.
Manual workflows eventually become difficult to scale.
As organizations grow, process complexity increases.
This is where the third pillar becomes critical.
Technology helps organizations operationalize and sustain compliance processes at scale.
Where does Technology Fit in the Compliance Management Strategy?
Technology is paramount in an effective compliance management program, but it must be used appropriately. A compliance management framework is incomplete without the right tool. Compliance management software aids in improving the efficiency of its operations and expanding its ability to manage and monitor the organization’s compliance risks. Some key areas where technological tools can be of particular use:
Pillar 3: Technology, Enabling Visibility, Automation, and Continuous Compliance
People establish accountability.
Processes create consistency.
Technology connects both and provides the visibility needed to manage compliance effectively at scale.
The third pillar of effective compliance management is Technology.
As organizations grow, compliance activities become more complex.
Teams may need to manage:
-
Multiple regulations
-
Hundreds of policies
-
Recurring obligations
-
Cross-functional approvals
-
Large volumes of evidence
-
Vendor oversight
-
Training requirements
-
Internal audits and corrective actions
Manual systems struggle to support this level of coordination.
Technology helps organizations centralize compliance activities and maintain ongoing oversight.
Why Technology Matters in Compliance Management
Many compliance programs still depend on spreadsheets, email reminders, and shared folders.
These tools may work temporarily, but they often create operational limitations.
Common challenges include:
-
No real-time visibility
-
Missing deadlines
-
Duplicate tracking
-
Limited reporting
-
Manual follow-ups
-
Version confusion
-
Evidence stored in multiple locations
As requirements expand, these problems become harder to manage.
Technology helps organizations move from fragmented tracking to centralized compliance operations.
Rather than chasing updates across teams, compliance leaders gain a clearer view of activities, ownership, and status.
What Compliance Technology Supports
Compliance technology supports far more than document storage.
Modern platforms help organizations manage the operational side of compliance.
Typical capabilities include:
-
Policy management
-
Workflow automation
-
Task assignment
-
Reminder and escalation management
-
Evidence collection
-
Audit preparation
-
Incident tracking
-
Dashboard reporting
-
Regulatory monitoring
-
Control and risk oversight
These functions improve coordination and reduce administrative effort.
Technology creates structure that supports both people and process.
Automation Reduces Manual Work
One of the largest advantages of compliance technology is automation.
Manual compliance management often depends on repetitive tasks.
Examples include:
-
Sending reminders
-
Tracking due dates
-
Collecting approvals
-
Following up on evidence
-
Updating spreadsheets
-
Preparing reports
These activities consume time and increase the risk of missed obligations.
Automation reduces this burden.
Examples of automated compliance workflows include:
-
Recurring compliance task scheduling
-
Policy review reminders
-
Training notifications
-
Approval routing
-
Escalation of overdue items
-
Audit preparation workflows
-
Evidence submission alerts
Automation does not replace human oversight.
Instead, it allows teams to focus on analysis, decision-making, and issue resolution rather than administrative follow-up.
Centralization Improves Visibility
Visibility is a major challenge in decentralized compliance environments.
When policies, controls, and records exist across multiple systems, organizations struggle to answer basic questions:
-
What is overdue?
-
Which policies need review?
-
Who owns this obligation?
-
What evidence is missing?
-
Which issues remain unresolved?
Without centralized visibility, compliance becomes reactive.
Technology helps consolidate information into a single operational view.
Centralized systems support:
-
Unified reporting
-
Cross-team collaboration
-
Easier audit preparation
-
Faster decision-making
-
Consistent documentation
This reduces uncertainty and strengthens oversight.
Technology Supports Continuous Compliance
Historically, many organizations approached compliance as a periodic activity.
Preparation increased before:
-
Audits
-
Regulatory reviews
-
Certification renewals
-
Board reporting cycles
This periodic model often creates rushed execution and documentation gaps.
Technology supports continuous compliance.
Continuous compliance means organizations maintain ongoing visibility into obligations and control performance rather than relying on periodic review.
Continuous monitoring may include:
-
Real-time task tracking
-
Control status monitoring
-
Dashboard reporting
-
Policy lifecycle management
-
Automated reminders
-
Exception reporting
This approach reduces last-minute preparation and supports stronger governance.
Data, Reporting, and Executive Oversight
Compliance leaders increasingly need data-driven reporting.
Executives and boards often ask:
-
Are we compliant?
-
Where are our biggest risks?
-
Which obligations are overdue?
-
What trends are emerging?
-
How effective are our controls?
Manual reporting makes these questions difficult to answer quickly.
Technology improves reporting through:
-
Dashboards
-
Trend analysis
-
Completion metrics
-
Audit logs
-
Risk indicators
-
Performance reporting
This provides leadership with better operational insight.
Instead of relying on anecdotal updates, teams can provide measurable compliance data.
Common Technology Gaps
Not all compliance technology delivers equal value.
Organizations sometimes face challenges such as:
| Technology Gap | Operational Impact |
|---|---|
| Poor usability | Low adoption |
| Limited integration | Data silos |
| Weak reporting | Reduced visibility |
| No automation | Administrative burden |
| Fragmented systems | Duplicate work |
| Inflexible workflows | Process inefficiency |
Technology should support operational execution rather than create additional complexity.
Usability and adoption are critical.
If teams avoid the platform, compliance visibility suffers.
How VComply Supports the Technology Pillar
Modern compliance management requires connected workflows and centralized oversight.
VComply helps organizations operationalize compliance by connecting people, process, and technology in one platform.
Organizations can use VComply to:
-
Assign compliance ownership
-
Automate recurring tasks and reminders
-
Centralize policies and documentation
-
Track evidence and approvals
-
Monitor compliance activities through dashboards
-
Maintain audit trails and reporting visibility
This approach helps teams move beyond spreadsheets and disconnected systems toward more structured and measurable compliance management.
Technology becomes most valuable when it strengthens execution rather than simply storing information.
However, even with strong technology, organizations may still face challenges if the three pillars are not balanced.
The next step is understanding how people, process, and technology work together and where organizations commonly struggle.
Choosing Technology That Supports People and Process
Technology is most effective when it reinforces the first two pillars.
Organizations should evaluate whether software helps:
-
Clarify ownership
-
Standardize workflows
-
Centralize policies
-
Automate reminders
-
Collect evidence
-
Support escalation
-
Improve reporting
-
Strengthen audit readiness
Technology alone does not create compliance maturity.
It works best when aligned with accountability and repeatable processes.
Best Practices for Building a Winning Compliance Management Program
A thorough compliance management system can be the biggest differentiator between successful and failed organizations in the present times. A compliance management program safeguards your organization from potential risk factors or emerging risks and compliance challenges. But building a compliance management program from scratch can be quite daunting. Here are the steps for building a successful compliance management program for your organization.
Conduct a Comprehensive Risk Assessment:
In most industries, regulatory standards are well-defined and serve as the basis of the compliance plan. Having said that, some hidden risk factors always emerge at later stages and might be critical to the compliance process. Based on your existing threats and business knowledge, you need to have a thorough compliance risk assessment plan ready to identify, monitor, and mitigate potential errors and threats.
Establish Company Policies and Procedures:
Compliance management is a top-down initiative where the leadership actively participates, and everyone becomes an equal stakeholder for regulatory readiness. Your compliance team will assume most of the responsibility for achieving and maintaining compliance. However, your program fails to reach its true potential without top-down buy-in.
Create a policy outlining the compliance-related roles and responsibilities for each department and team in your organization. In addition to this, set clear deadlines so your employees know what and when the outcomes are expected of them.
Communicate the Plan and Provide Training:
Remember that the greater the risk, the more intensive attention should be given to detail. Help employees understand the severity of compliance management and make the training simplistic for holistic inclusion. This can mean anything from bilingual training to providing concrete examples backed by use cases.
Adopt a Risk-Based Approach to Compliance Management:
A risk-based approach to compliance and ethics management involves identifying, assessing, and uncovering organizational high-priority risks. As a best practice, risk-based compliance programs enable organizations to capture, consolidate, and centralize risk management based on standards, controls, and actions.
By applying a risk-based approach across the organization, GRC professionals can present best practices to highlight the most serious compliance risks across the organization and showcase actions taken to mitigate issues, violations, investigations, and fines.
A standard risk-based approach includes:
- Keeping up with standards
- Ensuring that all employees understand the requirements
- Align business functions with compliance
- Identifying and rectifying violations as they happen to enhance the process
- Review processes and procedures at regular intervals
Invest in Compliance Management Software:
Catering to every risk factor and each potential error manually is an impossible task. With the constantly rising stakes, there is negligible room for error and experimentation. In such a pressing scenario, compliance management software like VComply can proactively manage the three critical aspects of your business: people, processes, and technology.
You should look for the following capabilities while going for compliance management software:
- Customizable according to the compliance obligation to meet your objective.
- You should be able to manage your compliance programs across multiple locations or business functions.
- You can generate user-friendly, real-time reports from unified dashboards.

How People, Process, and Technology Work Together
The three pillars of compliance management are interconnected.
Organizations often underperform when they prioritize one pillar while neglecting the others.
For example:
-
Strong technology without ownership creates poor adoption.
-
Skilled employees without defined processes create inconsistency.
-
Well-documented processes without technology become difficult to scale.
Effective compliance programs balance all three pillars.
The relationship can be viewed as:
| Pillar | Purpose | Common Gap | Operational Impact | How Technology Helps |
|---|---|---|---|---|
| People | Accountability and ownership | Unclear responsibilities | Missed obligations | Task ownership and reminders |
| Process | Consistency and governance | Informal workflows | Execution gaps | Workflow automation and approvals |
| Technology | Visibility and oversight | Fragmented systems | Limited reporting | Centralized dashboards and audit trails |
This balance creates operational alignment.
When people understand responsibilities, processes guide execution, and technology provides visibility, compliance becomes more sustainable.
Common Mistakes That Weaken Compliance Programs
Many organizations experience recurring compliance problems due to imbalance between the three pillars.
Recognizing these issues is the first step toward improvement.
1. Treating Compliance as a Department Rather Than a Business Responsibility
Some organizations place full responsibility on compliance teams.
While central oversight is necessary, compliance execution usually depends on multiple business functions.
This creates bottlenecks and limits accountability.
Compliance works best when ownership is distributed and supported by central governance.
2. Depending Too Heavily on Manual Tracking
Spreadsheets and email remain common.
However, manual systems often create:
-
Tracking errors
-
Missing reminders
-
Duplicate records
-
Limited reporting
-
Version confusion
Manual methods may support small programs but often become difficult to manage as requirements grow.
3. Building Processes That Are Too Complex
Excessive approvals and overly detailed workflows can slow execution.
Employees may bypass difficult procedures when systems create friction.
Effective processes should balance control and usability.
Simple, repeatable workflows often perform better than highly complex models.
4. Failing to Maintain Policy and Procedure Reviews
Policies often become outdated.
Without scheduled review processes, organizations may continue relying on obsolete guidance.
This creates regulatory and operational exposure.
Policy lifecycle management should include:
-
Ownership
-
Review schedules
-
Approval workflows
-
Version tracking
-
Acknowledgment monitoring
5. Measuring Activity Rather Than Effectiveness
Organizations sometimes focus on volume rather than outcomes.
Examples include:
-
Number of policies published
-
Training hours completed
-
Tasks assigned
These metrics matter, but they do not always reflect effectiveness.
Better indicators include:
-
Completion rates
-
Overdue trends
-
Control performance
-
Audit findings
-
Issue resolution speed
-
Policy acknowledgment rates
Performance-based measurement improves oversight.
How to Balance the Three Pillars
Building a mature compliance program requires deliberate alignment.
Organizations should evaluate whether each pillar supports the others.
A practical approach includes five steps.
Step 1: Define Ownership Clearly
Identify who owns:
-
Policies
-
Controls
-
Training
-
Reporting
-
Evidence collection
-
Corrective actions
Clear ownership reduces ambiguity.
Step 2: Standardize Core Compliance Processes
Document repeatable workflows for:
-
Policy approvals
-
Compliance tasks
-
Escalations
-
Incident management
-
Audit preparation
Standardization improves consistency.
Step 3: Centralize Information
Centralized systems improve visibility.
Organizations should avoid storing compliance information across disconnected tools whenever possible.
Centralization helps teams:
-
Locate evidence faster
-
Improve reporting
-
Reduce duplication
-
Maintain version control
Step 4: Use Automation Strategically
Automation should support recurring and administrative activities.
Examples include:
-
Reminders
-
Review schedules
-
Escalations
-
Approval routing
-
Notifications
Automation helps maintain consistency without increasing administrative burden.
Step 5: Review and Improve Continuously
Compliance programs should evolve.
Regular evaluation helps organizations identify:
-
Process bottlenecks
-
Ownership gaps
-
Technology limitations
-
Training needs
-
Reporting weaknesses
Continuous improvement supports long-term maturity.
Building a More Connected Compliance Program with VComply
The three-pillar model highlights an important reality.
Compliance does not succeed through policy documentation alone.
Organizations need connected execution.
VComply helps organizations strengthen compliance operations by supporting each pillar within a centralized environment.
People
-
Assigned ownership
-
Accountability tracking
-
Role-based responsibilities
Process
-
Standardized workflows
-
Approvals and escalations
-
Evidence collection and task management
Technology
-
Dashboards and reporting
-
Automated reminders
-
Audit trails and centralized visibility
This helps organizations manage compliance as an operational function rather than a fragmented collection of activities.
Final Thoughts
Effective compliance management depends on more than regulatory knowledge.
Organizations need the right combination of people, process, and technology.
People establish accountability.
Processes create consistency.
Technology enables visibility and scalability.
When these pillars operate together, organizations gain stronger oversight, improved audit readiness, better reporting, and greater confidence in their compliance programs.
As regulatory expectations continue to evolve, organizations that balance these pillars are better positioned to manage risk and maintain operational control.
The Role of Leadership in Sustaining Compliance Programs
Leadership commitment is one of the most critical factors in ensuring the long-term success of a compliance management framework. Executives and board members set the tone from the top, influencing how seriously employees view compliance. A leadership team that actively supports compliance initiatives—by allocating sufficient budgets, integrating compliance into strategic decisions, and publicly reinforcing accountability—helps embed compliance into the organizational DNA. Without visible leadership support, even the most advanced processes and technologies may fail to deliver the desired outcomes.
Continuous Monitoring and Improvement
Compliance is not a one-time initiative but an evolving discipline that requires continuous monitoring and refinement. Regulations change, new risks emerge, and organizations themselves expand into new markets and operations. A winning compliance management program therefore emphasizes periodic assessments, gap analyses, and feedback loops that allow businesses to stay agile. By treating compliance as a living framework rather than a static checklist, organizations can anticipate risks before they escalate and ensure that processes remain relevant and effective.
Integrating Compliance with Broader Risk Management
A strong compliance program cannot operate in isolation. Integrating compliance management with enterprise risk management, audit functions, and operational controls ensures that risk exposure is viewed holistically. This integrated approach allows organizations to identify overlaps between regulatory requirements and operational vulnerabilities, making risk mitigation more efficient. When compliance is tied to the larger risk management strategy, businesses can demonstrate resilience not only to regulators but also to investors, partners, and customers.
Building Trust with Stakeholders
Ultimately, compliance is about trust. Regulators want to trust that organizations will follow the law, customers want to trust that their data and interests are protected, and employees want to trust that they work in a transparent, ethical environment. A compliance management framework built on the pillars of people, process, and technology provides that assurance. With platforms like VComply, organizations can reinforce this trust by embedding compliance into their daily operations, providing transparency across functions, and ensuring a culture of accountability.
Conclusion
Though it might seem difficult and gruesome at a glance, you can strike a balance among all three components of the compliance management program with the help of a GRC platform. An effective compliance management framework can help you strategize in advance, safeguard your organization from heavy penalties, and build your credibility in the industry. With strong leadership support, continuous monitoring, integrated risk management, and the right technology, compliance becomes more than just meeting requirements—it becomes a foundation for long-term trust and sustainable growth.
Whether you’re aiming for managing multiple frameworks at multiple sites and maintaining continuous compliance, VComply can be trusted. VComply is the #1 GRC software trusted by compliance-forward organizations in various industries in 2025. Book a live demo to see how VComply can simplify your compliance journey.
Frequently Asked Questions
The three pillars of compliance management are people, process, and technology. Together, they create accountability, standardize execution, and improve visibility across compliance activities.
People are responsible for carrying out compliance obligations, following policies, collecting evidence, and maintaining accountability. Clear ownership improves execution and reduces missed obligations.
Processes create repeatable workflows that standardize approvals, evidence collection, escalation, and reporting. They help organizations maintain consistency and audit readiness.
Technology supports compliance by centralizing information, automating reminders, improving reporting, and providing real-time visibility into tasks, policies, and controls.
Compliance can operate manually, but manual systems often become difficult to manage as organizations grow. Technology helps improve scalability, reporting, and oversight.
Common weaknesses include unclear ownership, poor communication, manual tracking, inconsistent processes, outdated policies, and fragmented reporting systems.
Organizations can balance these pillars by defining ownership, documenting workflows, centralizing information, automating repetitive tasks, and continuously reviewing performance.
VComply helps organizations manage compliance through centralized workflows, task ownership, policy management, reminders, evidence tracking, dashboards, and reporting capabilities that support people, process, and technology together.